Role modelling and mining
Entitlement analysis, business role hierarchy design, birthright definition and role lifecycle governance.
SailPoint IdentityIQ, IdentityNow and Saviynt specialists building role models, certification campaigns, segregation-of-duties enforcement and the evidence chain your regulators expect.
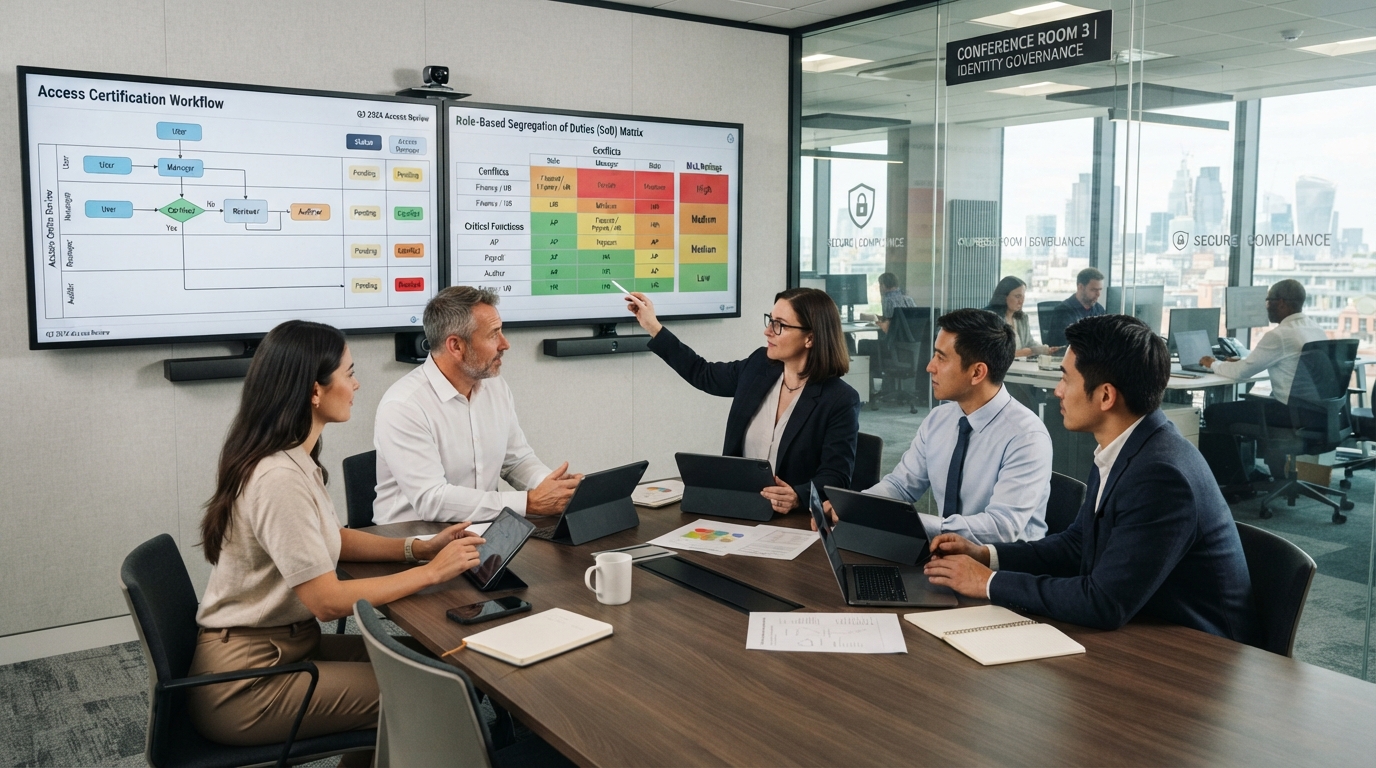
IGA work lives or dies on clean joiner-mover-leaver workflows and defensible access certifications. Our specialists have sat across the table from auditors, not just built the policy engine in isolation.
Every capability below is staffed by engineers who have executed it in a production enterprise estate.
Entitlement analysis, business role hierarchy design, birthright definition and role lifecycle governance.
Campaign design, scoping, launch automation, reviewer enablement, chase cycles and revocation processing.
SOD matrix construction, rule engine implementation, violation remediation workflow and exception governance.
Out-of-box and custom connector build, aggregation tuning, provisioning policy and reconciliation logic.
HR-driven joiner-mover-leaver workflows, delegated administration and automated deprovisioning assurance.
Control-mapped reporting, campaign evidence packs, access analytics and management dashboards.
Select any sub-service to open a pre-filled enquiry. Your requirement is emailed to our practice desk for same-day response.
Rules, workflows, task and quicklink development, connector configuration and performance tuning.
SaaS platform configuration, virtual appliance setup, transforms and cloud connector deployment.
Application onboarding, analytics and control build, SOD rules, campaigns and workflow configuration.
Migration between governance platforms with role model translation and campaign continuity.
Access request front-ending, approval routing and ticket lifecycle synchronisation.
Building connectors for in-house and niche applications with no vendor-supplied integration.
Structured waves of application integration with aggregation, provisioning and certification enablement.
Data-driven analysis of existing entitlements to propose a maintainable business role model.
Campaign calendar, reviewer strategy, scope tiering and reviewer fatigue mitigation.
Risk definition workshops, matrix construction, detection implementation and remediation workflow.
Identifying unowned and unused access, driving revocation and preventing recurrence.
Access risk scoring, trend reporting and executive dashboards for identity risk posture.
Design authority for role model, campaign strategy and platform roadmap.
Developers delivering connectors, workflows and rules against a sprint backlog.
Offshore pod running campaigns, processing revocations and maintaining connectors.
Short-term surge capacity to close access certification findings before a deadline.
Aggregation performance, rule hygiene, campaign efficacy and upgrade readiness assessment.
Closed cohort development and administration training for internal teams.
A repeatable sequence refined across hundreds of deployments.
Application prioritisation, entitlement data quality assessment and authoritative source confirmation.
Role hierarchy, birthright rules, SOD risk definitions and campaign strategy agreed with business owners.
Connector development, workflow configuration and provisioning policy implemented and tested.
A limited-scope certification run to validate reviewer experience and data quality before enterprise launch.
Application waves, campaign automation and lifecycle workflow rollout with reporting.
Ongoing campaign operations, model maintenance and continuous evidence generation for audit.
Send the requirement and receive vetted profiles, with recorded lab evidence, inside 48 hours.