Network and infrastructure testing
External and internal penetration testing with exploitation, privilege escalation and lateral movement analysis.
Penetration testing, red teaming, Active Directory attack path analysis and API security testing — with findings written for engineers who must fix them, not just for a compliance folder.
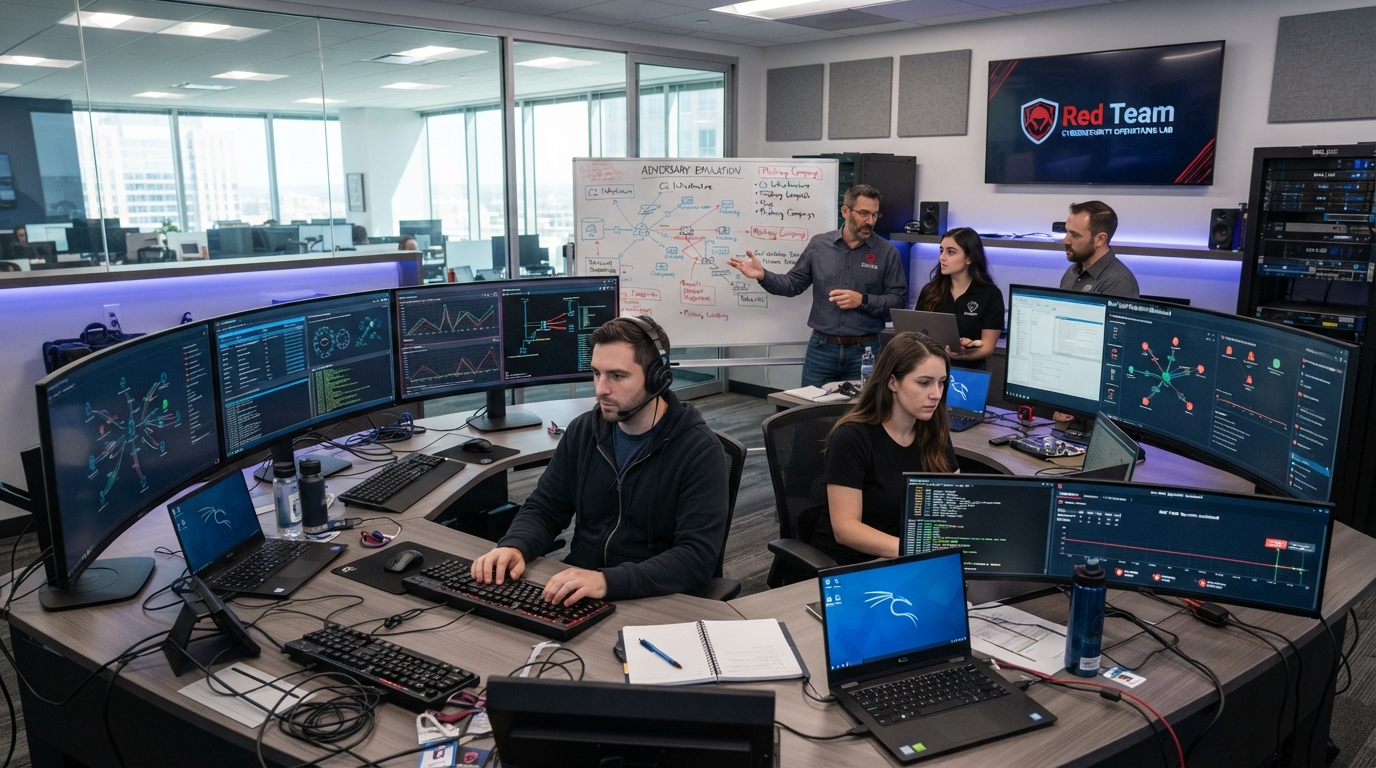
From scoped penetration tests to full adversary-emulation red team engagements, our offensive security bench reports findings the way your blue team can actually act on — with clear reproduction steps, not just a scanner dump.
Every capability below is staffed by engineers who have executed it in a production enterprise estate.
External and internal penetration testing with exploitation, privilege escalation and lateral movement analysis.
OWASP-aligned application testing, business logic abuse, authentication and authorisation flaw discovery and API-specific attack paths.
Kerberoasting, delegation abuse, ACL analysis, tier-model validation and attack path mapping to sensitive assets.
AWS, Azure and GCP configuration and identity abuse testing, privilege escalation paths and key exposure analysis.
Objective-based adversary emulation with optional purple mode where your defenders tune detections live against the operation.
Structured retesting after fixes, with a clear closure statement suitable for audit and customer assurance packs.
Select any sub-service to open a pre-filled enquiry. Your requirement is emailed to our practice desk for same-day response.
Internet-facing perimeter assessment covering exposed services, authentication surfaces and misconfiguration.
Assumed-breach assessment of lateral movement, privilege escalation and segmentation effectiveness.
Authenticated and unauthenticated testing against OWASP Top 10 and business logic abuse cases.
REST and GraphQL testing covering authorisation flaws, rate limiting, token handling and data exposure.
iOS and Android assessment covering storage, transport, binary protections and backend interaction.
Wireless network attacks and, where scoped, physical access and social engineering assessment.
Multi-week operation against defined crown-jewel objectives with realistic tradecraft and stealth requirements.
Collaborative attack and detect cycles with measured improvement in detection and response coverage.
Starting from a compromised workstation to test containment, detection and privilege boundaries.
Emulating precursor behaviours and testing backup, containment and recovery response.
Controlled campaigns with awareness measurement and credential-capture pathway analysis.
Executing an ATT&CK technique library against your SIEM and EDR to measure true coverage.
Scheduled testing calendar across applications and infrastructure with trend reporting.
Integrated into release cycles so findings arrive before production, not after.
Triage, prioritisation and remediation tracking with asset owners across scan output.
Manual and tool-assisted review of security-sensitive code paths with developer-ready guidance.
Structured design-phase analysis with your architects to remove classes of flaw early.
Hands-on support for engineering teams fixing complex findings, not just a report handover.
A repeatable sequence refined across hundreds of deployments.
Targets, objectives, constraints, escalation contacts and legal authorisation documented and signed.
Passive and active information gathering within agreed scope boundaries.
Systematic assessment with real-time notification of critical findings rather than waiting for the report.
Findings written with reproduction steps, business impact and specific remediation guidance.
Technical walkthrough for engineers and a separate executive summary session for leadership.
Verification of fixes with an updated report and a closure statement for audit purposes.
Send the requirement and receive vetted profiles, with recorded lab evidence, inside 48 hours.